Incidents & Threat Trends

Explore smartphone photography incidents, insider threats, AI agents and physical security trends, with practical screen data protection considerations.

Incidents & Threat Trends
|
10 min read

The OpenAI Security Case: Security Must Extend to the Physical World

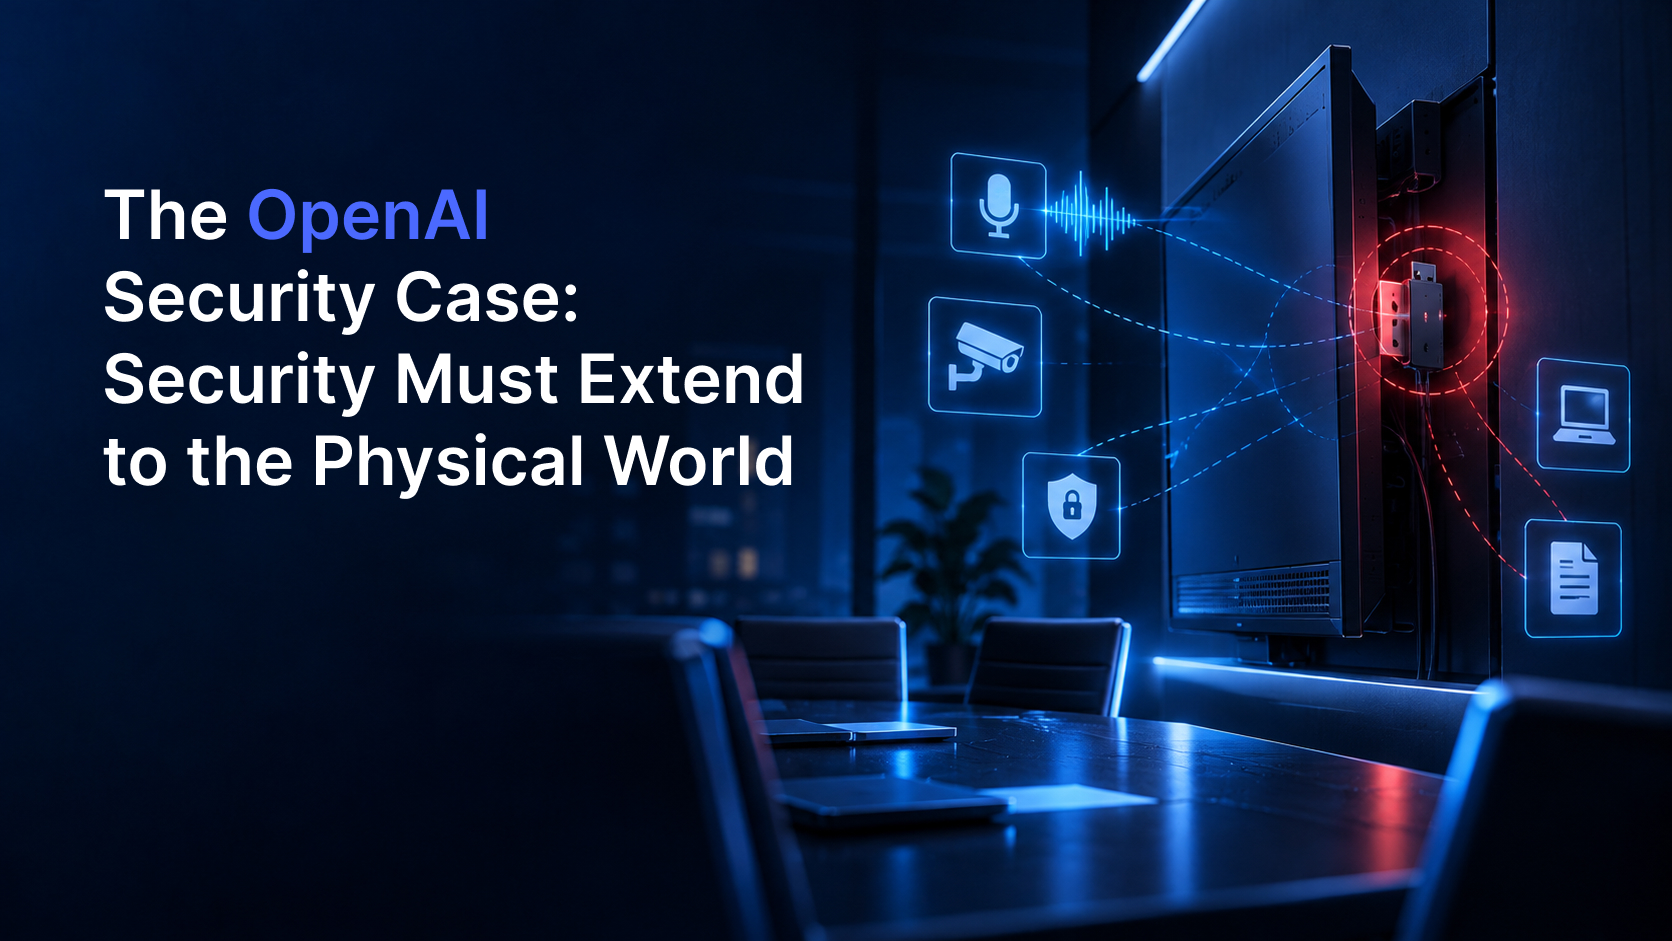
Imagine a conference room where teams discuss important research and product strategy. Even with restricted document access and controls on file transfers from company PCs, what happens if a small recorder hidden behind the television captures the conversation?

The discovery of a recording device at OpenAI, disclosed in October 2026, brought this question into focus. According to the U.S. Department of Justice, a concealed recorder was found plugged into a USB port behind a television in an OpenAI conference room. An employee was arrested on a charge of using or attempting to use a device to unlawfully intercept conversations.

Should this be treated as an exceptional incident limited to an advanced AI company? Other businesses also hold valuable information in their conference rooms and on employees' PCs. Product discussions, screens displaying customer information, and devices placed near work equipment all create potential points of exposure.

Enterprise security must address both online data movement and information gathering in the physical world. This case is a reason to consider endpoint security alongside the environment in which devices are used, as well as the files and processes running inside them.
Incidents & Threat Trends
|
13 min read

How AI Agents Expand Data-Leak Paths—and Why Screen Photography Prevention Matters

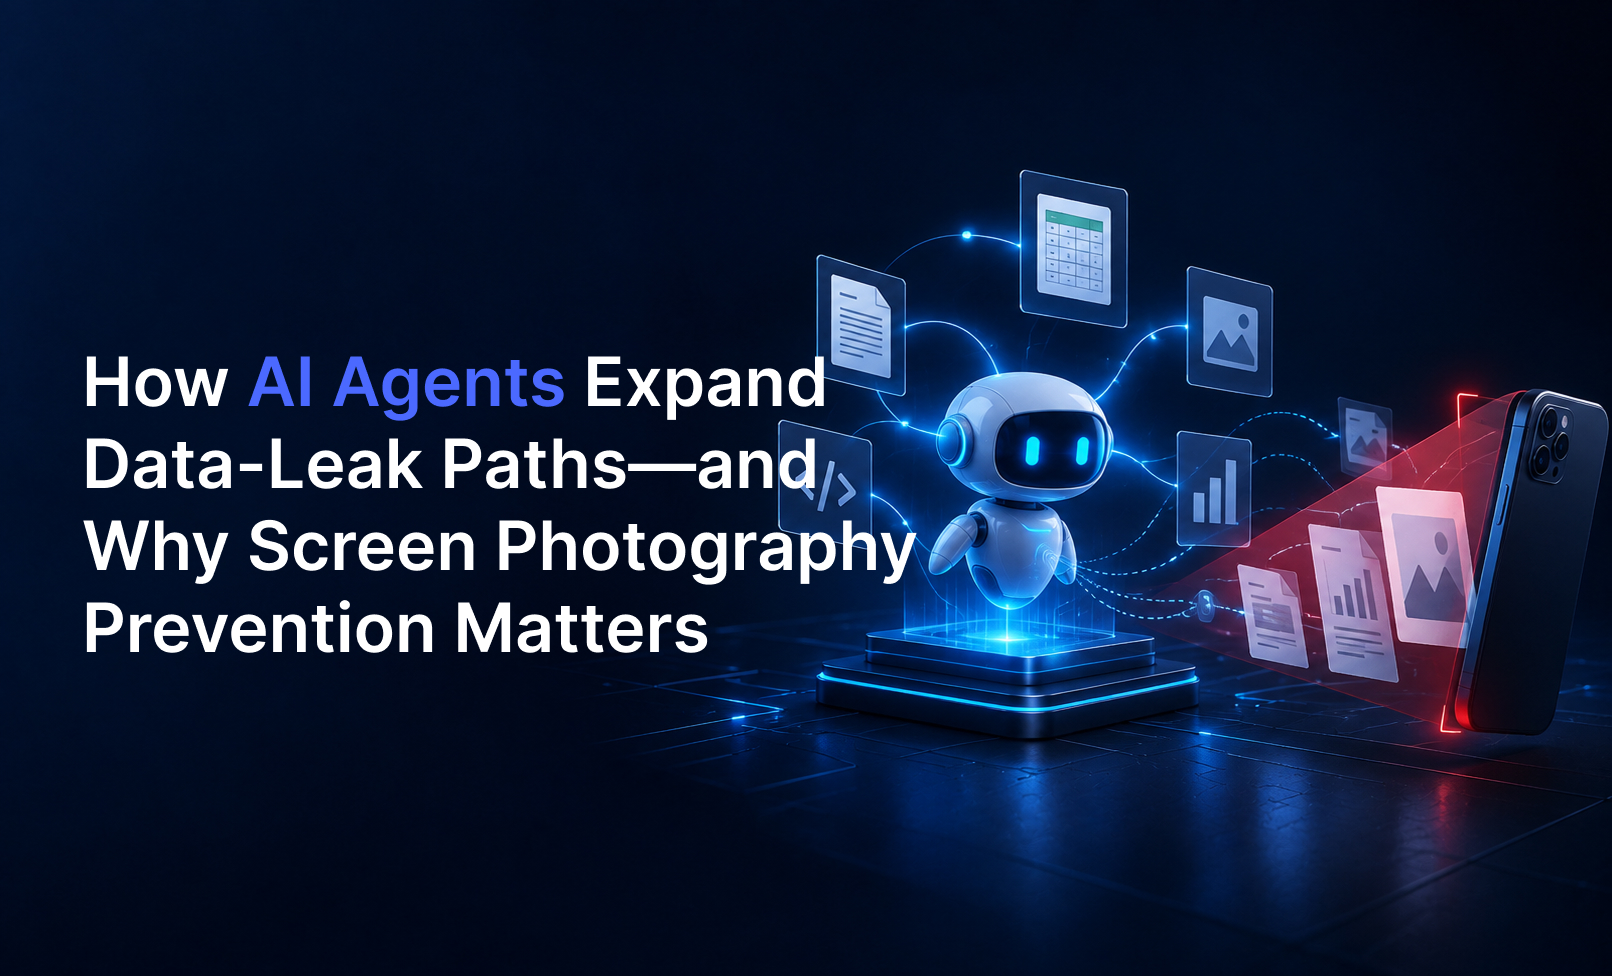
Generative AI is evolving from a tool that answers questions into an agent that performs work directly. Instead of simply summarizing a document supplied by a user, it can read files, open a browser, call external services, and save or share the results.

That improves productivity, but it also expands what security teams must monitor. In the past, the primary questions were which files a user downloaded and where they sent them. Now teams must also determine what data an AI agent accessed, which tools it used, and what it sent to which external services.

Existing channels such as USB copies, messaging apps, screen captures, and smartphone photography of monitors have not disappeared. AI has added new paths while the old methods of data exfiltration remain. This is why organizations should not treat AI agent security as a problem that a single product can solve. They need to reassess the entire data lifecycle—from storage and movement to use and final display on a screen.